
The Breach, the Theft and the Audit Start at the Same Door, Three Dental Experts Say

Left to right: dental revenue cycle expert Monica Cappelli, cybersecurity specialist Anthony Jurjevic, CISSP, and former Texas Dental Board investigator Duane "Tink" Tinker, co-authors of The Unlocked Practice.
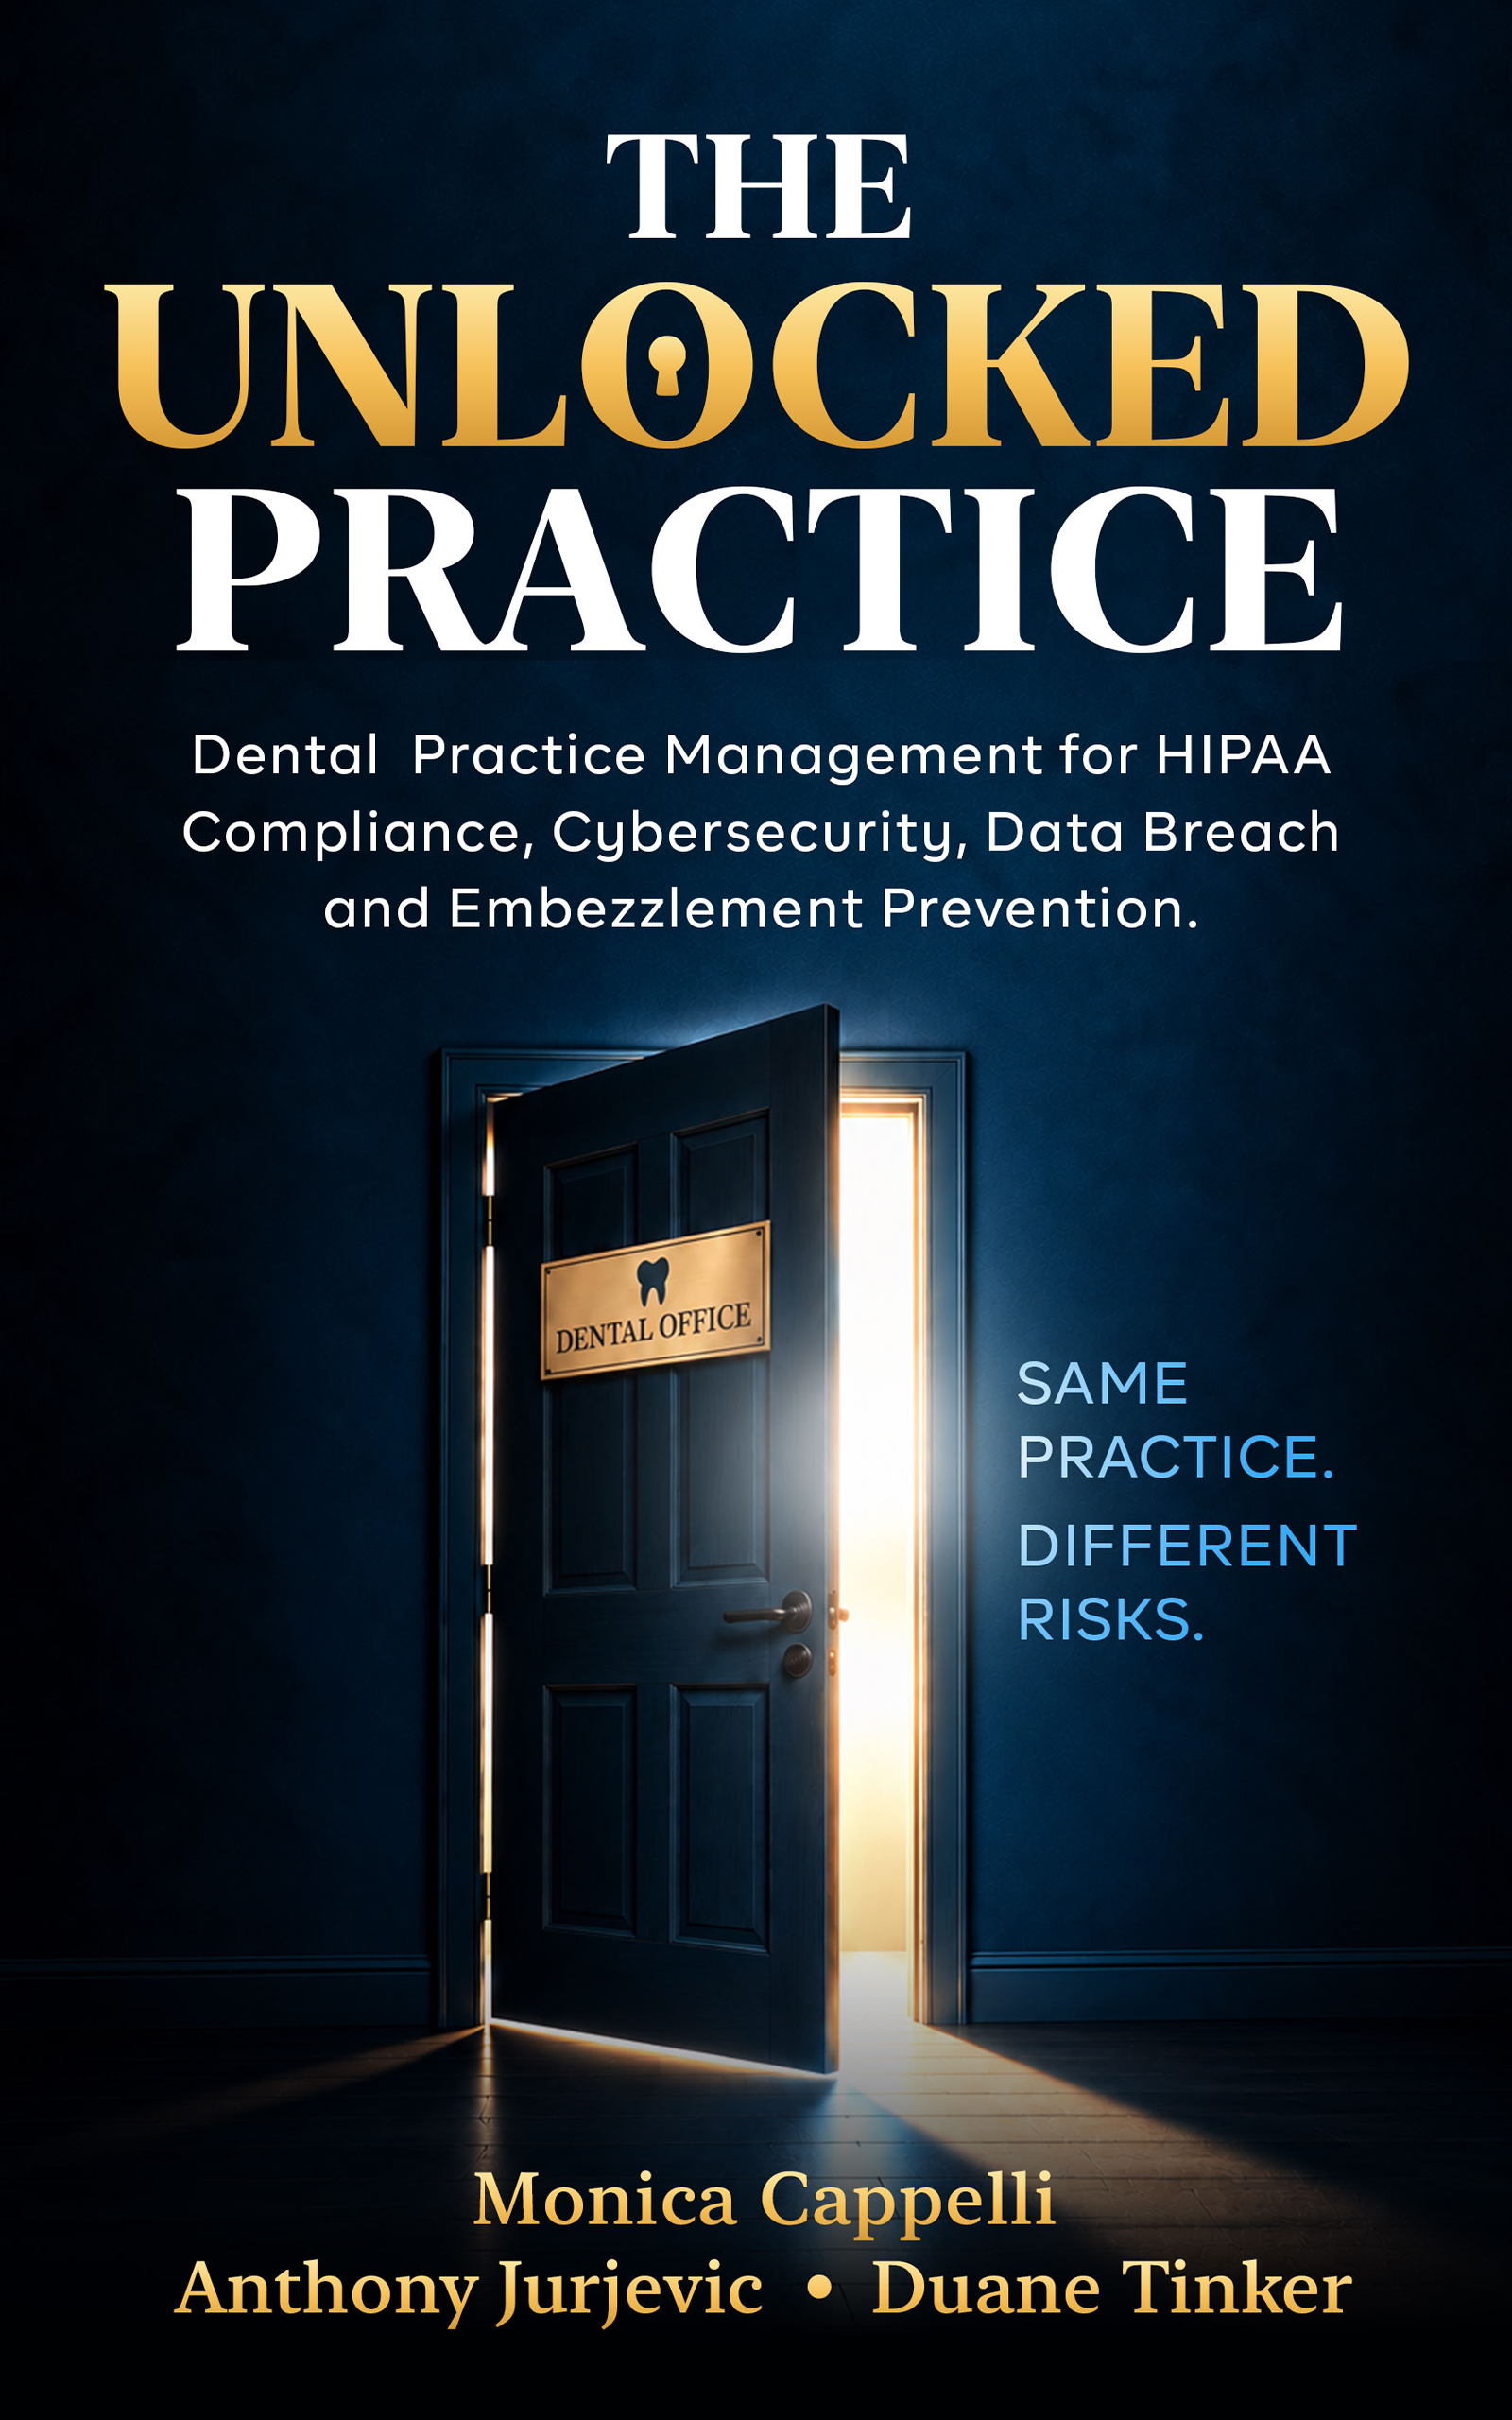
The Unlocked Practice: Dental Practice Management for HIPAA Compliance, Cybersecurity, Data Breach and Embezzlement Prevention, now available in paperback and Kindle on Amazon.
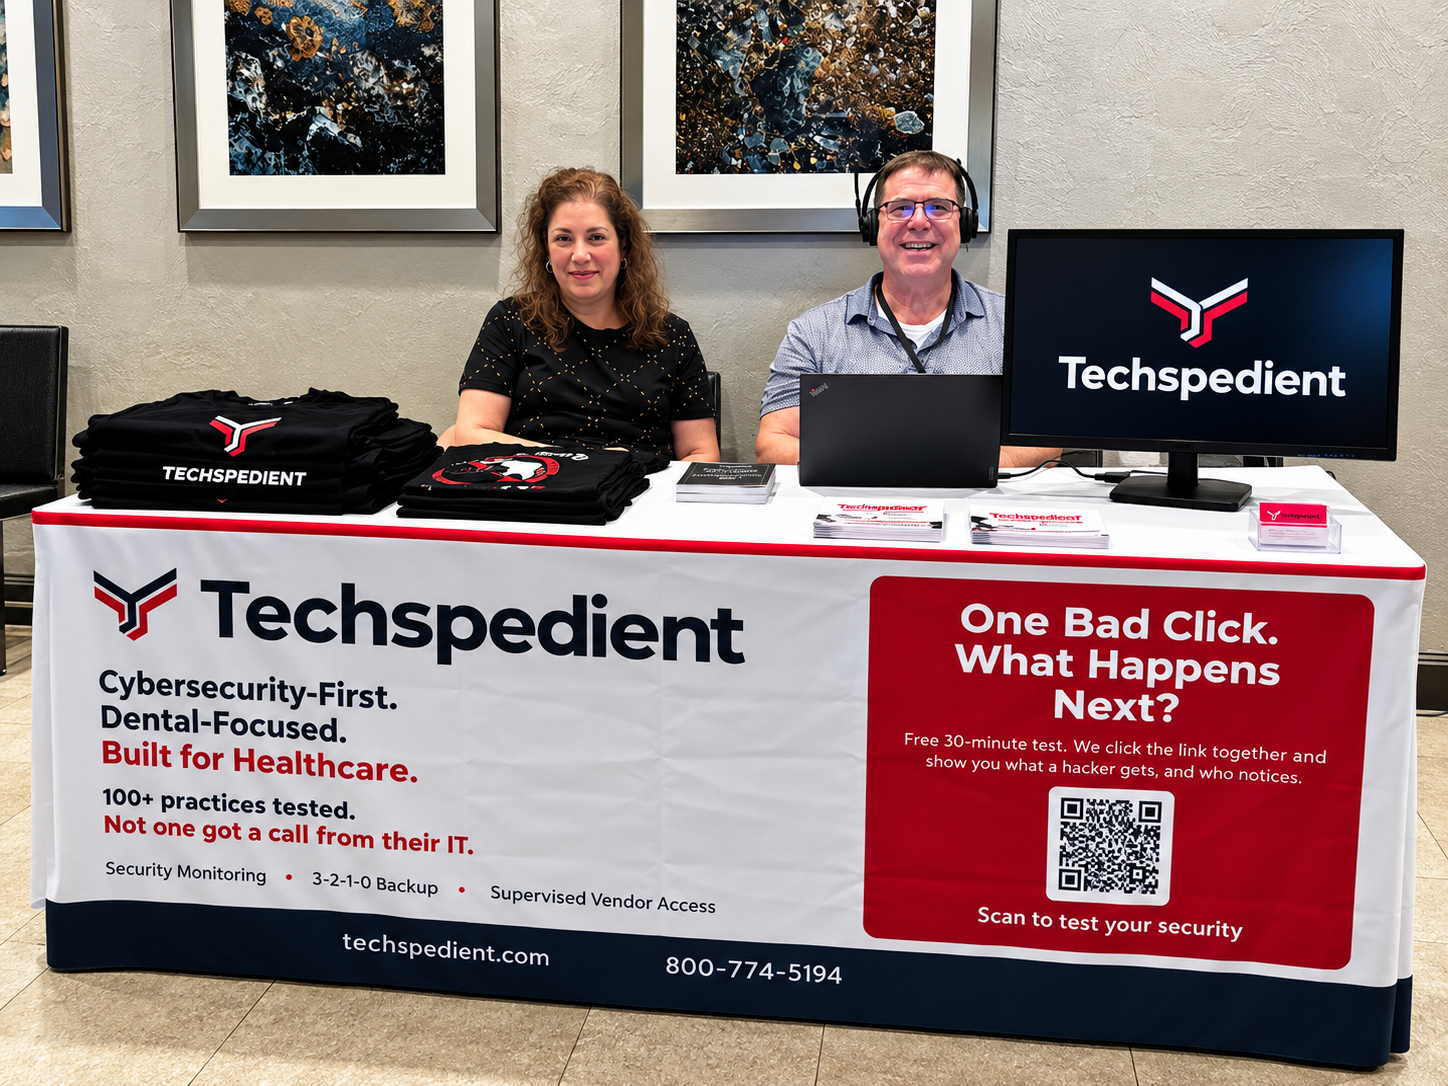
Co-author Anthony Jurjevic, CISSP, and the Techspedient team at a dental industry trade show, demonstrating how one phishing click exposes a practice.
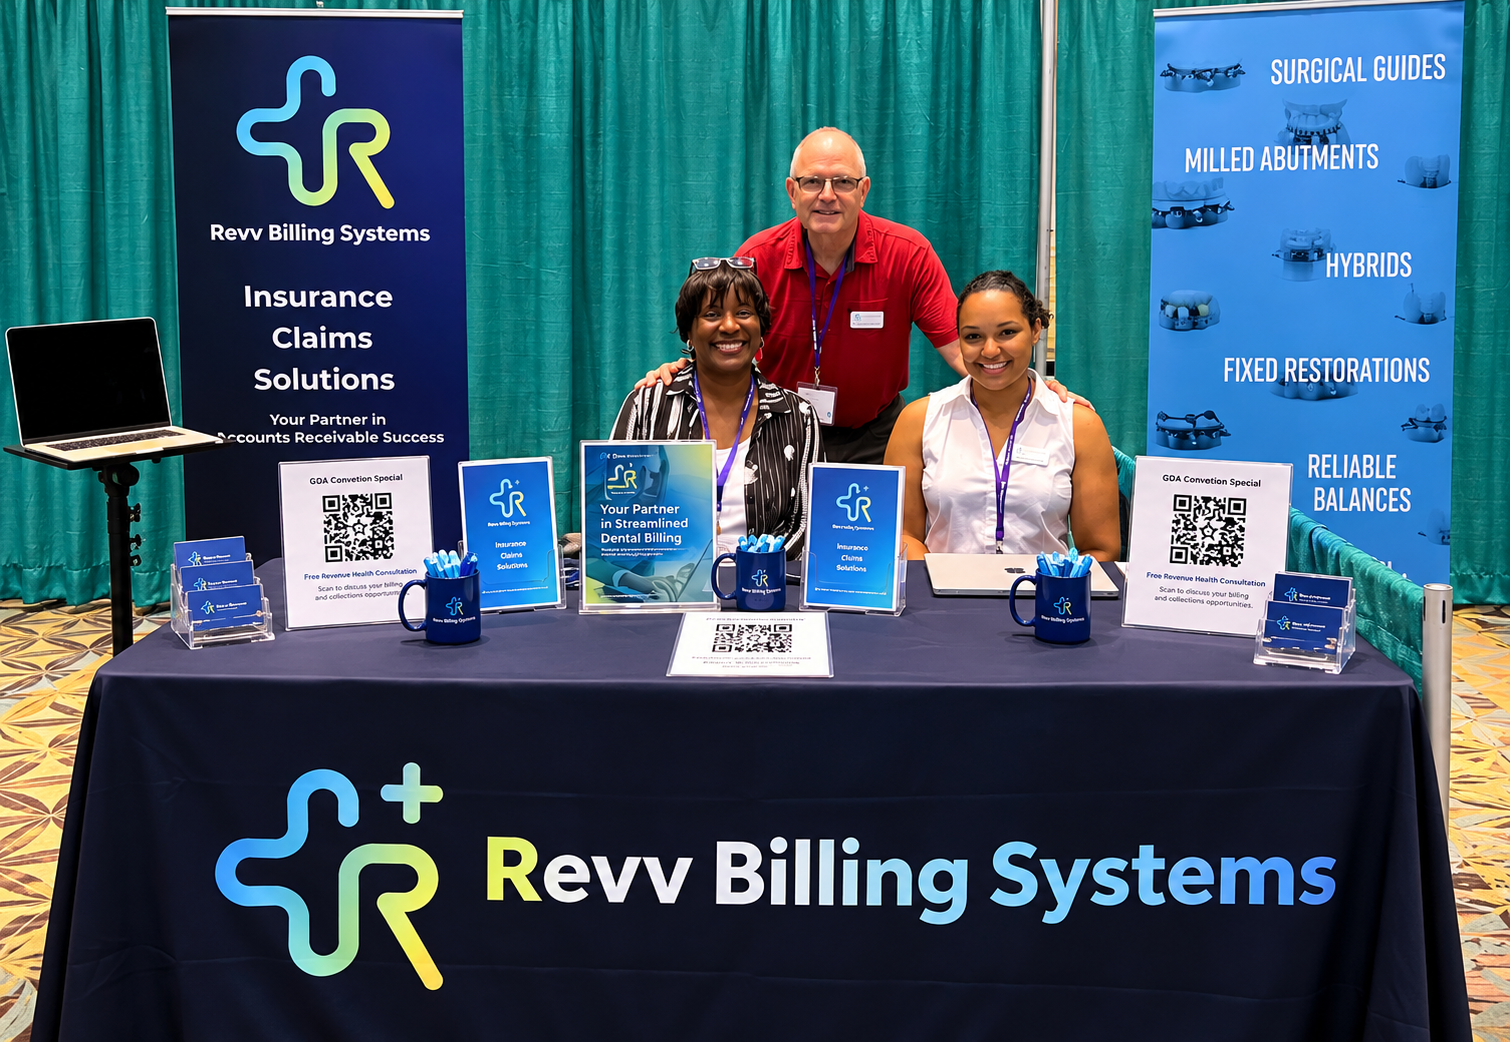
Revv Billing Systems at a dental industry trade show. Co-author Monica Cappelli founded the dental billing and revenue cycle firm whose work underpins her chapters in The Unlocked Practice.
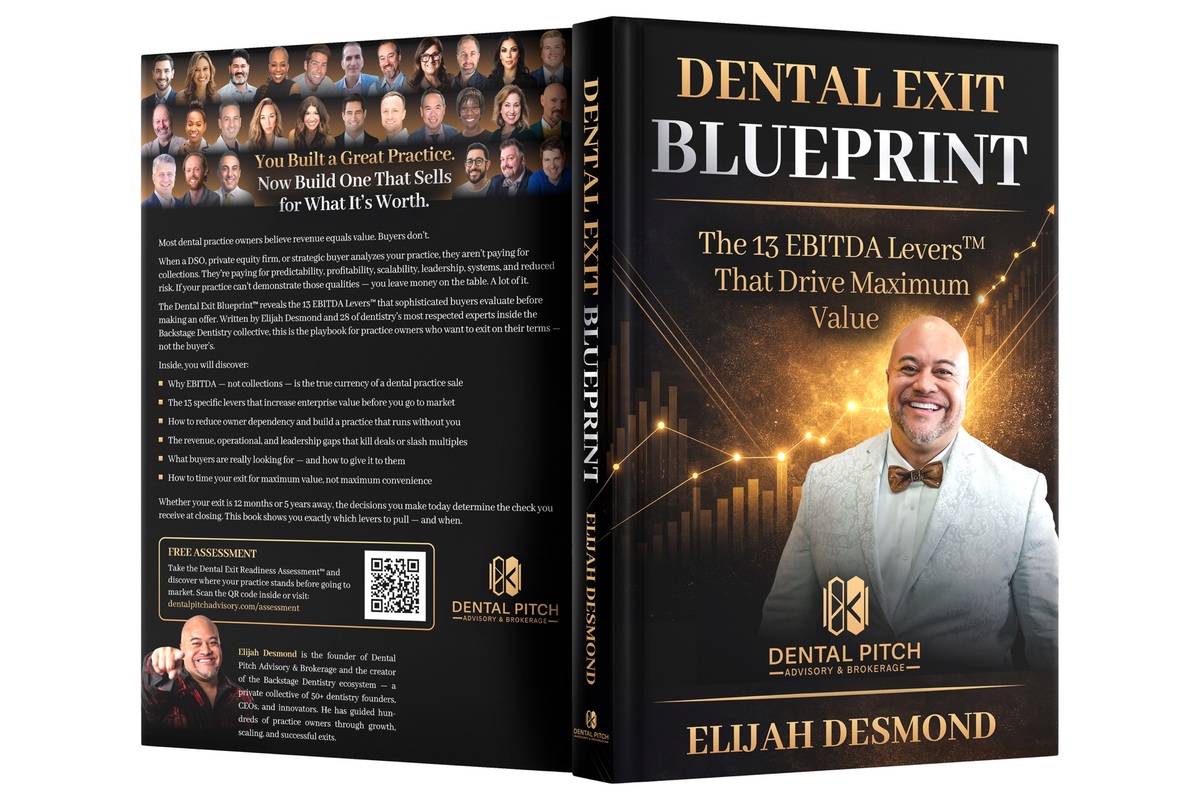
Co-author Monica Cappelli also contributed to The Dental Exit Blueprint, writing Lever 2, Collect More From Insurance, one of thirteen EBITDA levers that drive dental practice valuation.
A dental practice holds Social Security numbers, insurance files and payment data with none of a bank's oversight. Three specialists offer a 90-day plan.
The Unlocked Practice, released this month, is written by three specialists. Monica Cappelli, a practice management and revenue cycle expert, covers operations, vendor oversight and the reports that surface billing leakage and theft. Anthony Jurjevic, CISSP, covers remote access and the vendor connections owners cannot see. Duane "Tink" Tinker, a former Texas Dental Board law enforcement officer, covers documentation, claims integrity and what investigators look for.
More than 15 million people were notified this year that their information was exposed in a single dental benefits breach. The DentaQuest incident was reported by multiple security outlets as the largest U.S. health data breach disclosed in 2026. A dental record typically carries a Social Security number, an insurance identifier, a payment method and a medical history in one file.
A former employee's login that still works is a security exposure, a theft opportunity and a recordkeeping problem at once, and no one department owns it. The book documents the pattern across 78 endnotes drawn from federal enforcement actions, embezzlement prosecutions and appellate decisions involving dentists.
In simulated phishing tests Jurjevic's firm ran at more than 100 dental practices, not one practice's IT provider called to ask about it, he reports.
The theft side is not confined to healthcare. In Occupational Fraud 2026, the Association of Certified Fraud Examiners' global study, the median case ran twelve months before anyone detected it, and 43 percent were found through a tip rather than by a control. Organizations with fewer than 100 employees posted the highest median loss of any size band, $126,000.
“Nobody creates the underlying facts. The investigator does not. The payer does not. Looking only reveals what was already there.”
Duane "Tink" Tinker
Six steps the authors recommend this month:
1.Ask your IT provider, in writing, for every person, vendor and tool that can reach your systems from outside the building. Note how many entries are question marks.
2.Turn on multifactor authentication everywhere, starting with email, because whoever controls email can reset nearly every other password.
3.Have the owner receive bank and merchant statements directly, not through the person who reconciles them.
4.Require five consecutive business days away for anyone who handles money. A process only one person can run is one no one else can check.
5.Pull five charts at random and confirm the clinical record supports the claim submitted.
6.Close accounts the day someone leaves, and verify it rather than assume it.
“Most owners are not careless. They are busy. The distance between assuming a practice is protected and knowing it is protected is where the risk lives.“
Monica Cappelli
Cappelli's revenue integrity chapters extend work she began as a contributing author of the bestselling dental business book The Dental Exit Blueprint, where she wrote Lever 2, Collect More From Insurance, one of thirteen EBITDA levers behind practice valuation. Owners can score their practice across all thirteen with the Dental Exit Readiness Score at dentalexitscore.com.
The book's eleven questions for evaluating a dental IT provider are posted free at unlockedpractice.com, with no registration required. The Unlocked Practice is available in paperback and Kindle on Amazon.
About Monica Cappelli
Monica Cappelli is a dental practice management and revenue cycle expert with nearly three decades in the industry and founder of Revv Billing Systems, a dental billing firm serving practices nationwide. She created RevvConnect Coaching, RCM Genius and PPO Genius, and is a contributing author of The Dental Exit Blueprint, where she wrote Lever 2, Collect More From Insurance.
About Anthony Jurjevic, CISSP
Anthony Jurjevic is the founder and president of Techspedient, a cybersecurity-first IT company serving dental and healthcare practices nationwide and a Microsoft Advanced Partner. He has spent 25 years in enterprise IT and cybersecurity, the last decade on the systems dental practices run daily, and holds the CISSP, the field's most widely recognized security certification.
About Duane "Tink" Tinker
Duane Tinker is a dental compliance and risk management consultant and a former Texas Dental Board law enforcement officer who investigated hundreds of cases involving standard of care, infection control, drug diversion and fraud. After 30 years as an EMT, he helps dental organizations protect their patients, teams and licenses through compliance systems, inspections and training.
Catrise Austin
Celebrity Branding, LLC
+1 917-540-5367
Dental Compliance Specialists with Howard Farran and Duane Tinker
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
